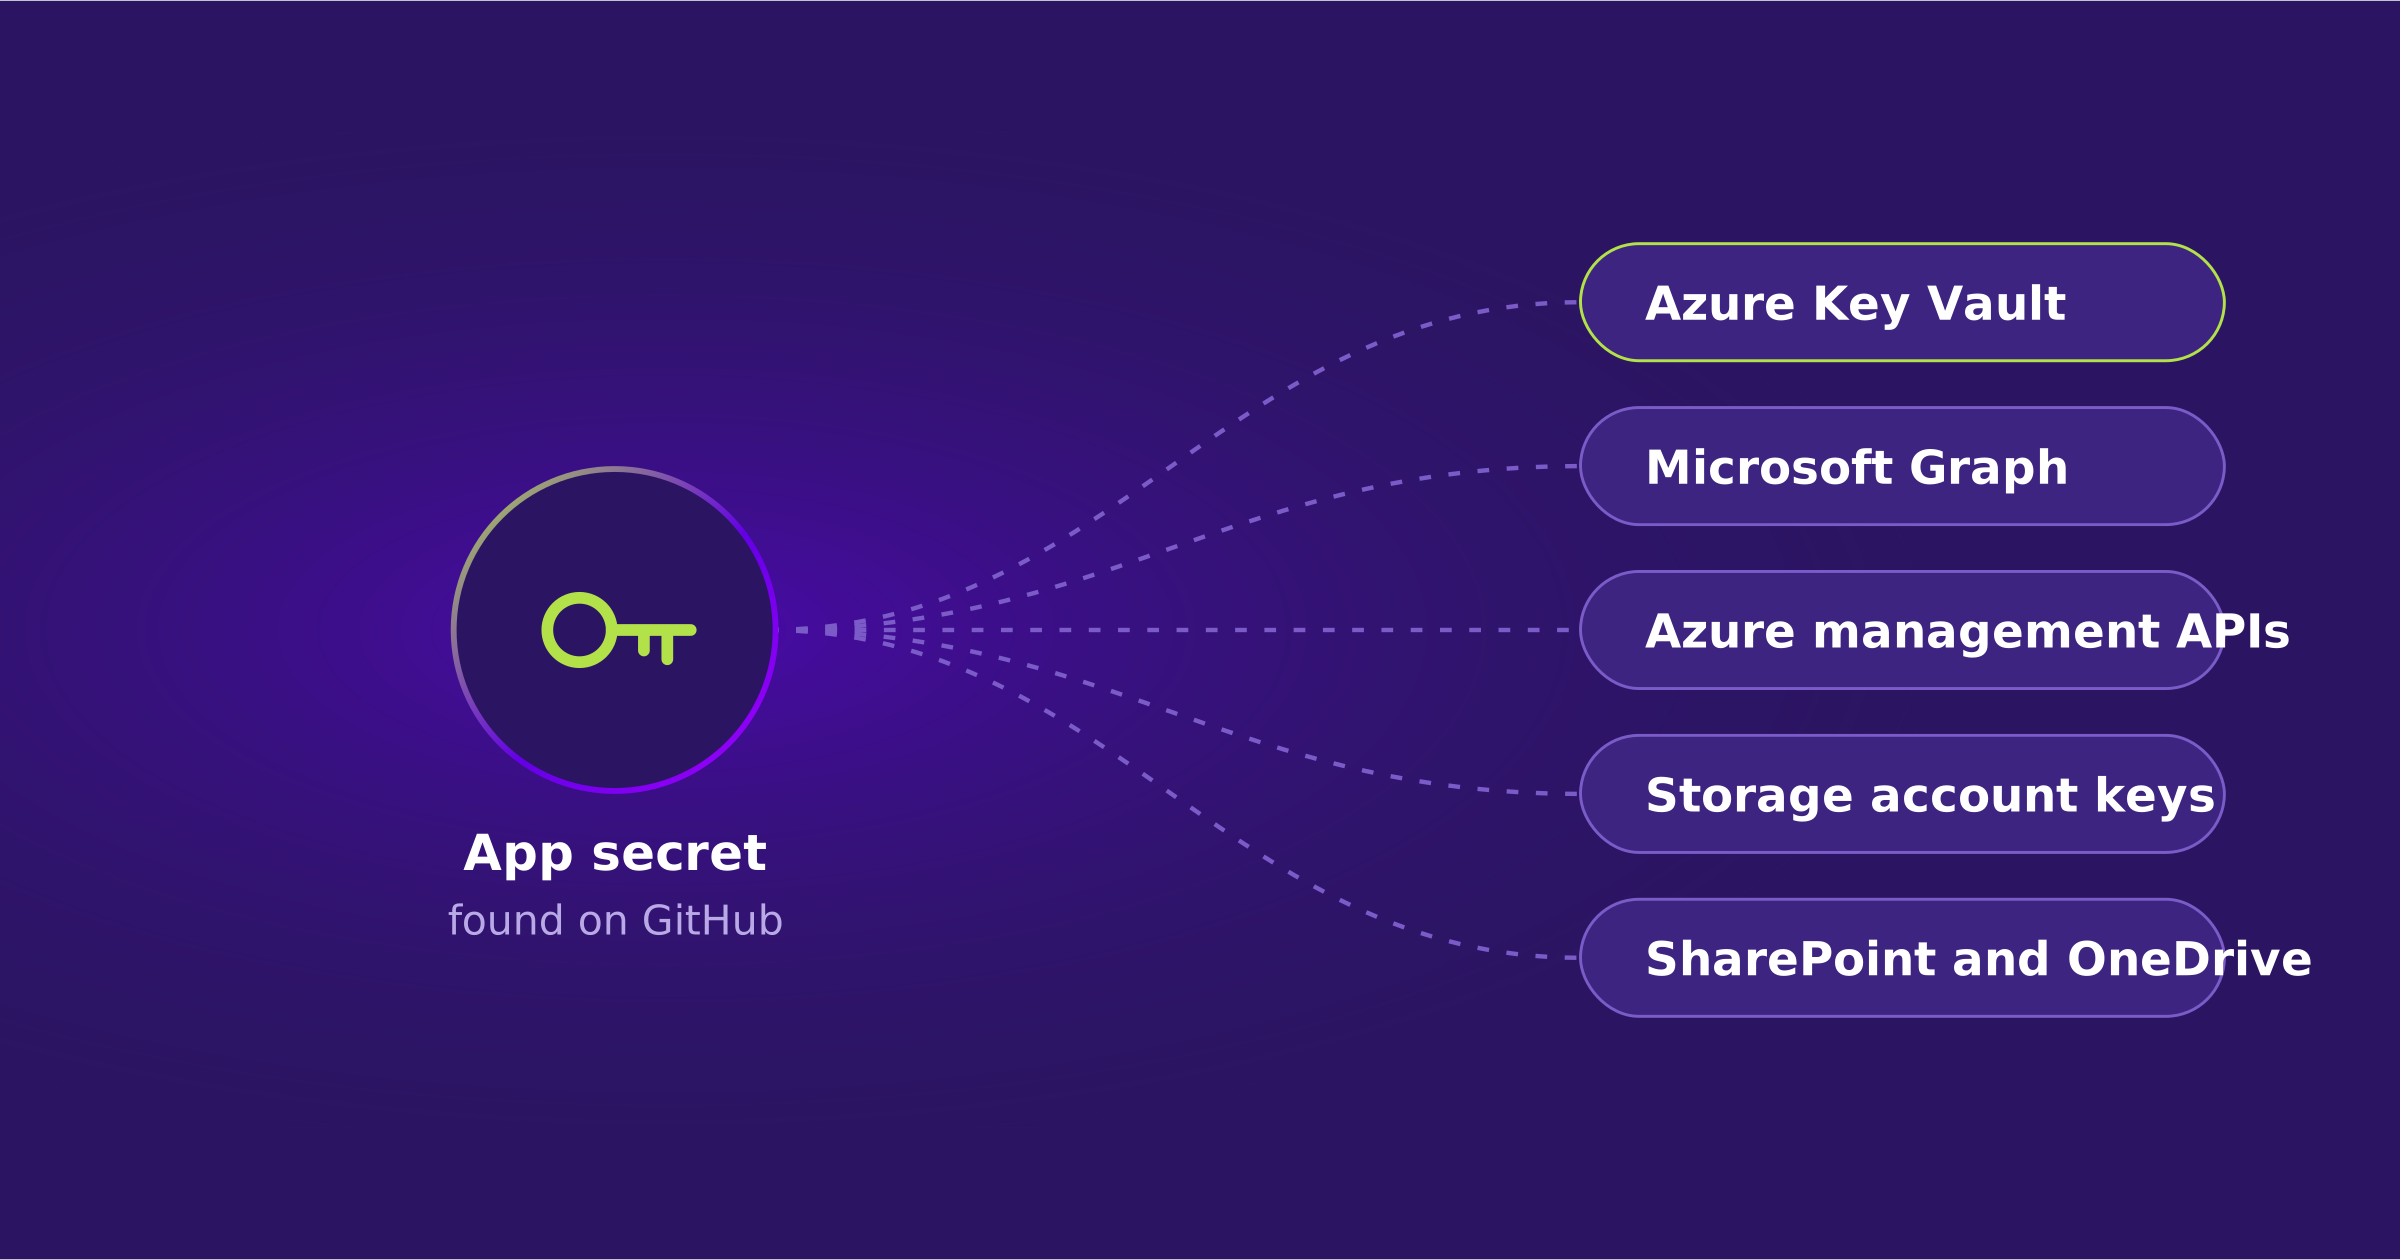
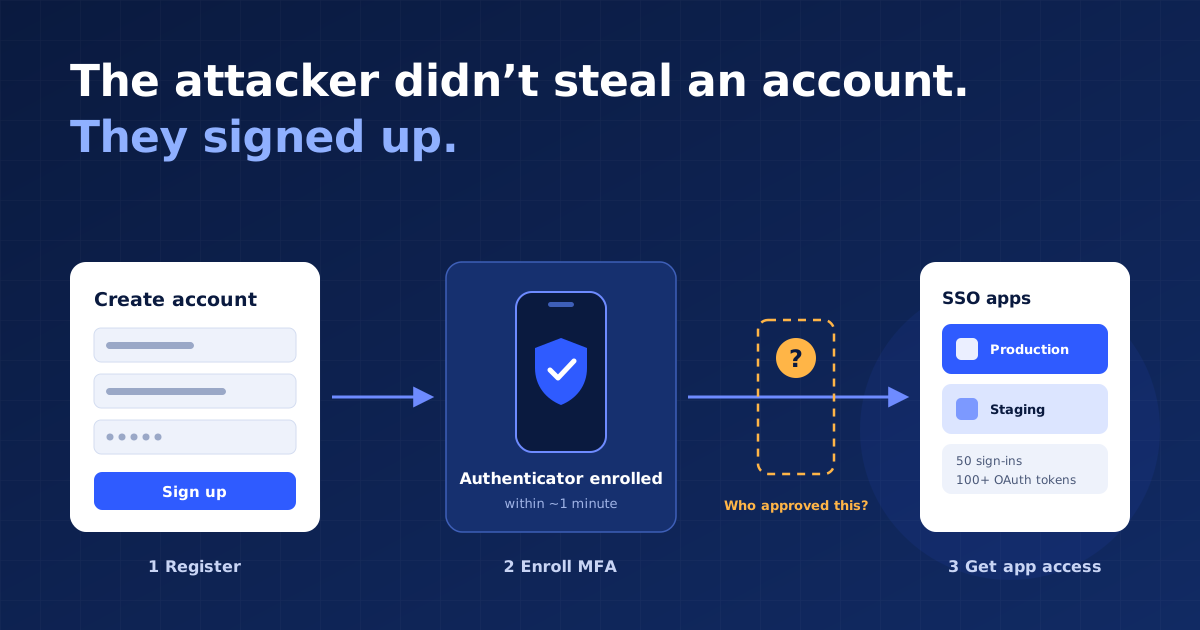
Blog Release Notes White Papers Use Cases Solution Briefs Videos Blog Release Notes White Papers Use Cases Solution Briefs Videos Resources / Blog Blog Field notes from the teams keeping identity recoverable: incidents worth studying, regulation worth tracking, and what we are building. Featured One Leaked App Secret. How Many Other Keys Can It Reach? TL;DRRotating a leaked application secret fixes the credential, not the exposure. While the secret worked, anyone holding it could sign... November 12, 2026 Read more → The Attacker Didn’t Steal an Account. They Signed UP TL;DR Between October 13 and 14, an attacker used self-service registration in a customer’s Okta environment to create five accounts,... How Far Can One Stolen Identity Reach? How Far Can One Stolen Identity Reach? | IAM, Segmentation & Identity Recovery | Acsense Skip to content TL;DR Network... The Backups Were There. The Restore Wasn’t. The Backups Were There. The Restore Wasn’t. | ConnectWise Incident & Identity Recovery | Acsense TL;DR On October 15, 2026,... A Small Distinction With Large Consequences: Action, State and Outcome Action, State, Outcome: Verifying Automated Identity Changes – acsense Look Past the Green Check Mark Verifying an automated identity change... When Identity Breaks, Everything Breaks: monday.com’s Lessons in Identity Resilience When Identity Breaks, Everything Breaks | Acsense What Happens to a Business When Identity Stops Working? Users never report that... You Revoked the Token. What Did the Attacker Leave Behind? Look Beyond the Original Credential Identity incident recovery is the work of finding and correcting every access change an attacker... Acsense Joins Oktane 2026 as Gold Sponsor Acsense joins Oktane 2026 as a Gold Sponsor, showcasing its Observe, Assure, Act, Restore, Verify model for stopping identity attacks... The Agent Is Gone. The Change Is Still There AI agents get shut down in seconds, but the changes they make can linger for days. Identity security needs recovery,... IAM Disaster Recovery: Four Days Isn’t a Safe Window See why a four-day exploit window makes IAM disaster recovery essential, and why Git alone can't restore trust after an... Page1 Page2 Page3 … Page18